TL;DR
- Cursor said on November 13 that an access key it had issued to inference vendor Fireworks AI was exposed by Fireworks and used to copy coding-agent traces from a shared storage bucket. Some traces contained unredacted credentials.
- On October 29, an attacker used a stolen credential from that path to place malicious copies of Anthropic's Claude Code extension, versions 2.1.312 and 2.1.313, into the cache that serves Cursor's marketplace. The copies were available for about 11 hours, between about 2:27 a.m. PT and 1:35 p.m. PT.
- Cursor said at most 5,000 users who requested those cached versions that day potentially received the malicious build. Anthropic did not publish the copies. The Open VSX marketplace source never had the malware.
- Cursor said the last attacker activity it has seen was on November 1. That activity was blocked. The company believes the incident is contained.
- Anyone who installed or updated those versions from Cursor's marketplace during that window should follow Cursor's security notice. Uninstalling the extension alone may not be enough.
Cursor published a detailed update on November 13 about a security incident that reached its VS Code extension marketplace. The company said an attacker obtained an access key Cursor had issued to Fireworks AI, its inference vendor. Cursor said Fireworks exposed that key. The attacker used it to copy data from a read-only storage bucket that Cursor used to share information with the vendor.
That bucket held limited coding-agent traces, mostly from 2025. The traces came from sessions that were not in Privacy Mode. Cursor said it was permitted to use those sessions for model training. A small number of the traces contained credentials that had not been redacted. Cursor said less than 0.01% of customers had API credentials exposed. Starting with those credentials, the attacker reached some of the SaaS tools Cursor uses internally.
On October 29, the attacker used a stolen credential from that exposed data to place malicious, unauthorized copies of Anthropic's Claude Code extension directly on the cache that serves Cursor's marketplace. The tampered versions were Anthropic.claude-code 2.1.312 and 2.1.313, for Windows and macOS. Cursor said Anthropic did not publish those copies. The company said this was not a vulnerability in Anthropic's product. The marketplace source, Open VSX, never had the malware.
Cursor's security notice said the malicious copies were available between about 2:27 a.m. PT and 1:35 p.m. PT on October 29. That window lasted approximately 11 hours. Cursor said at most 5,000 users who requested those specific cached versions that day potentially received the malicious build. The notice said the extension attempted to collect host information and install a persistent SSH backdoor. Cursor removed the copies. It took the marketplace offline. It worked with the cloud provider hosting the attacker's server to take that server down.
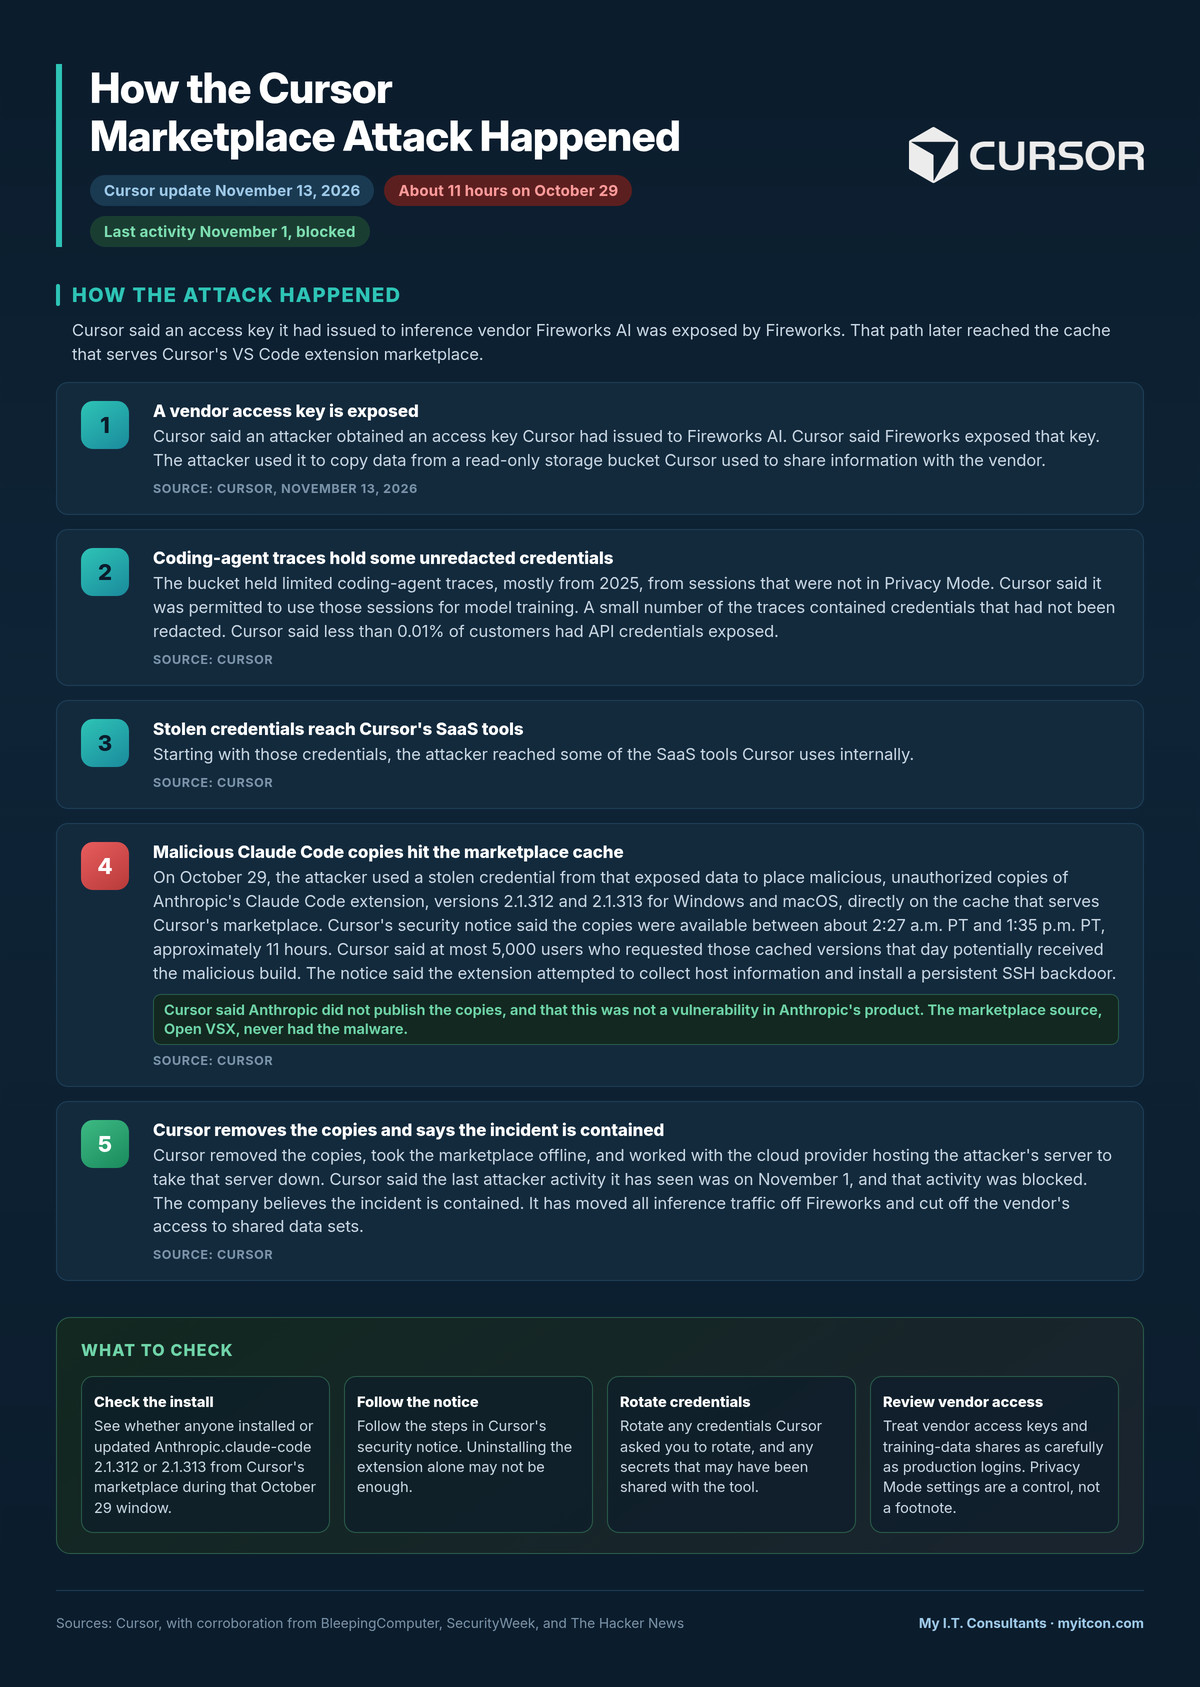
Cursor said the last attacker activity it has seen was on November 1. That activity was blocked. The company believes the incident is contained. It has moved all inference traffic off Fireworks. It deactivated the vendor key. It cut off the vendor's access to shared data sets. Customers who may have been affected were notified.
If your shop uses Cursor, check whether anyone installed or updated Anthropic.claude-code 2.1.312 or 2.1.313 from the Cursor marketplace during that October 29 window. Follow the steps in Cursor's security notice. Uninstalling the extension alone may not be enough. Rotate any credentials Cursor asked you to rotate. Treat vendor access keys and training-data shares as carefully as you treat production logins. Privacy Mode and similar data-sharing settings are a control, not a footnote. The same lesson applies to other SI coding tools that send traces or secrets to a vendor.
Chandler businesses can ask veteran-owned My I.T. Consultants in Athens for a Free Assessment. As a Microsoft-certified MSP, we can review the SI coding tools and vendor access in your environment. Call 903-675-5431. Our office hours for hourly work are Monday through Friday from 7:00 a.m. to 6:00 p.m. Contract customers can reach us 24/7.
Want help with this at your business? See Cybersecurity on our Services page or contact My I.T. Consultants.
Image: My I.T. Consultants