TL;DR
- Fandango Media is notifying customers who bought movie tickets on its website from October 8 to 11, 2026. An unauthorized party could access payment card information on the checkout page.
- The data may include the card number, CVV, expiration date, billing ZIP code, and email address. Names, government IDs, Social Security numbers, and other account information were not involved.
- Fandango says it has fixed the checkout page and is not aware of fraud. It is offering 24 months of free IDX monitoring, with an enrollment deadline of February 13, 2027.
- Fandango has not published a nationwide total. Oregon's registry lists 913 residents, and Vermont's lists 18.
- Anyone who bought tickets in that window should watch their statements. Businesses that take cards online should use hosted payment fields and inventory the scripts on checkout.
Fandango Media is notifying customers who bought movie tickets on its website from October 8 to 11, 2026. The company's official notice says an unauthorized party could access payment card information entered on the checkout page during those four days. Fandango determined on October 30 that some customers' information may have been affected. BleepingComputer reported on November 16 that card-skimmer code had been injected into that checkout page.
The information that may have been taken includes the payment card number, the CVV security code, the expiration date, the billing ZIP code, and the email address. Fandango says names, government-issued identification, Social Security numbers, and other account information were not involved. Those card details can still be used for unauthorized online purchases.
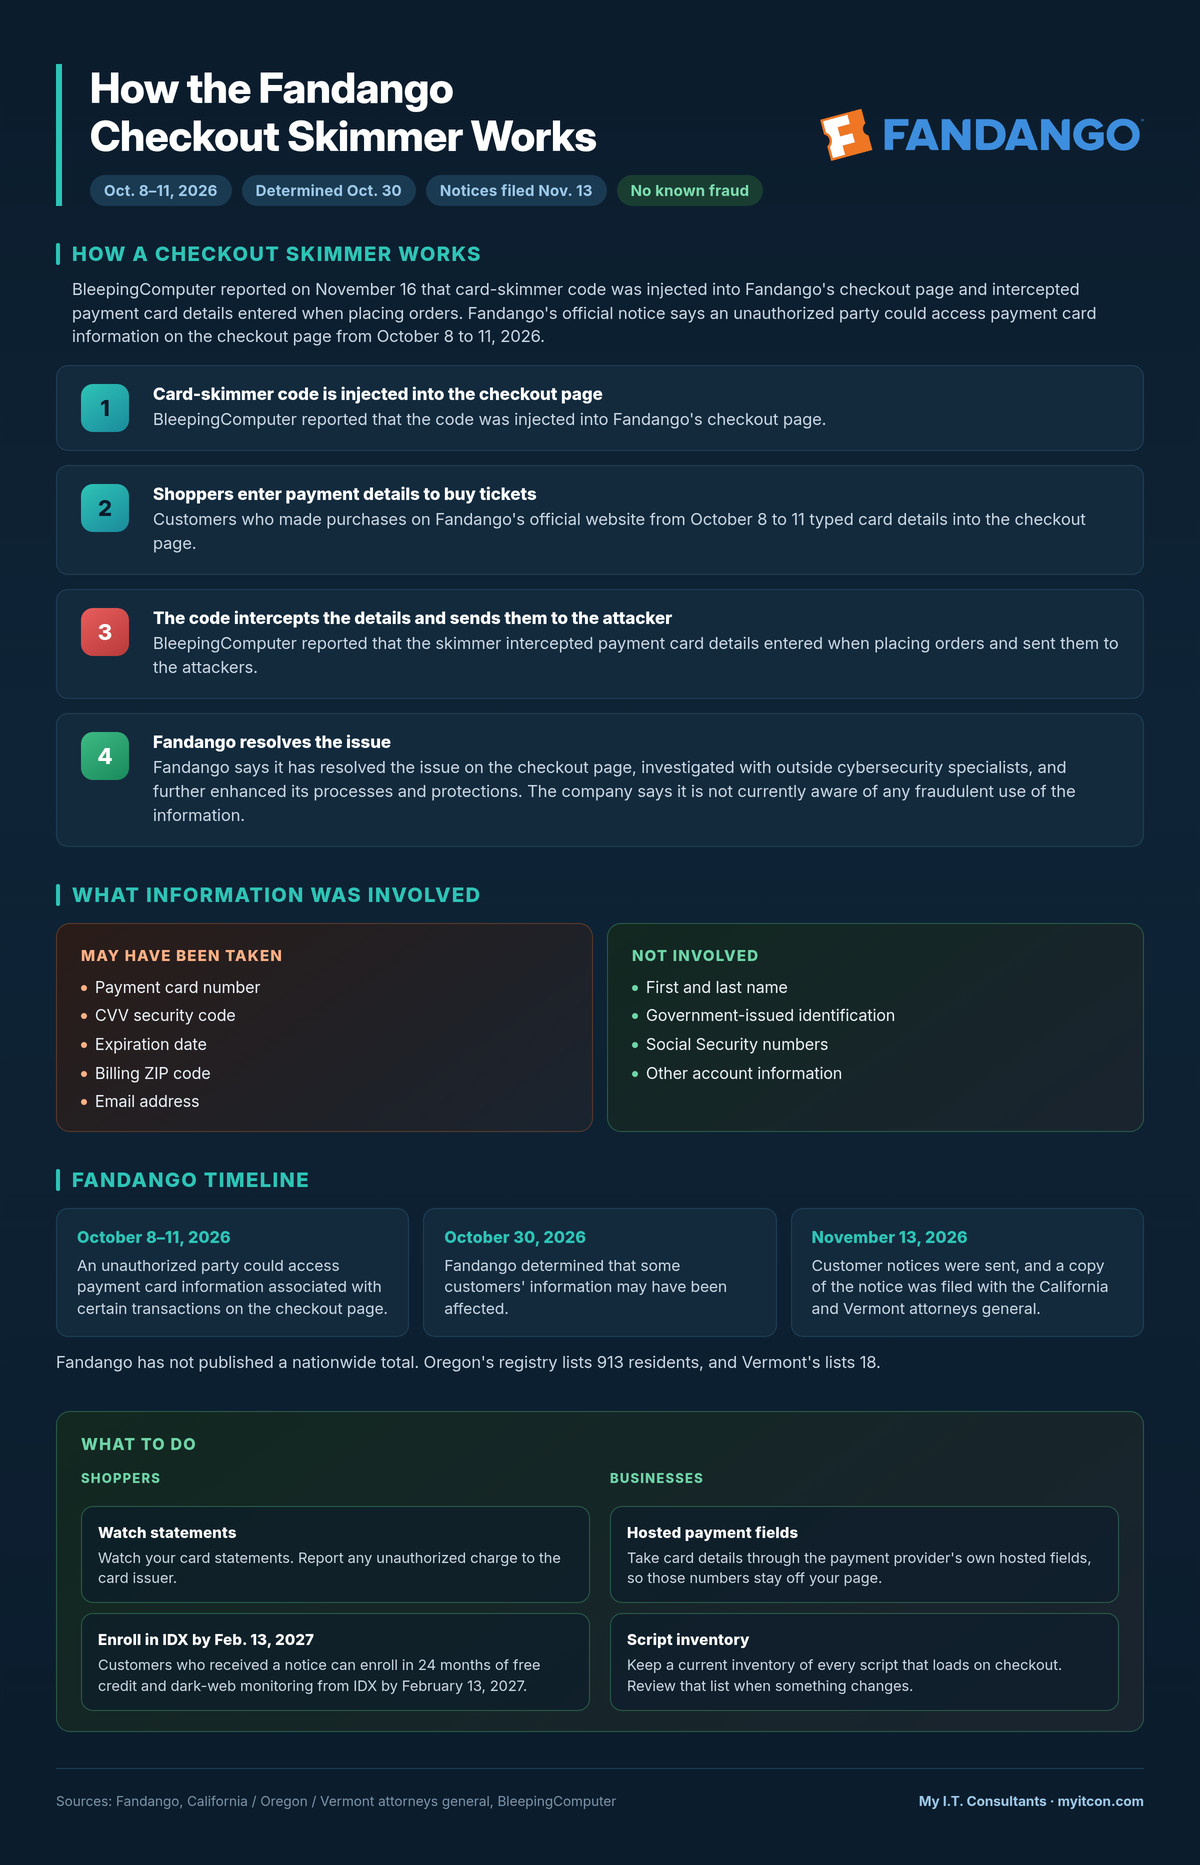
Fandango says it has resolved the issue on the checkout page. It investigated with outside cybersecurity specialists. It has further enhanced its processes and protections. The company says it is not currently aware of any fraudulent use of the information. It is offering affected customers 24 months of free credit and dark-web monitoring from IDX, along with identity theft recovery services. The offer also includes a $1,000,000 insurance reimbursement policy. The enrollment deadline is February 13, 2027.
Fandango has not published a nationwide total of affected customers. A filing with the Oregon Department of Justice lists 913 Oregon residents. A filing with the Vermont Attorney General lists 18 Vermont residents. A copy of the customer notice was also filed with the California Attorney General on November 13.
Anyone who bought tickets on Fandango's website from October 8 to 11 should watch their card statements. Report any unauthorized charge to the card issuer. Customers who received a notice can enroll in the free monitoring before the February deadline.
Businesses that take cards online can reduce this risk on their own sites. A skimmer copies what a shopper types into a payment form on the page. Payment fields hosted by the card processor keep those numbers off your page. Keep a current inventory of every script that loads on checkout. Review that list when something changes. Those steps close a door that a checkout page otherwise leaves open.
Mabank businesses can ask veteran-owned My I.T. Consultants in Athens for a Free Assessment. As a Microsoft-certified MSP, we can review the payment page on your website with you. Call 903-675-5431. Our office hours for hourly work are Monday through Friday from 7:00 a.m. to 6:00 p.m. Contract customers can reach us 24/7.
Want help with this at your business? See Cybersecurity on our Services page or contact My I.T. Consultants.
Image: My I.T. Consultants, with the official Fandango logo identifying the company in the story.