TL;DR
- Infoblox confirmed on Monday, November 16, that attackers reached company information through a compromised third-party data migration vendor.
- TechCrunch reported that an Infoblox notification described a SharePoint data-migration vendor. The Register, citing sources, said the vendor's accounts were used to copy data from SharePoint. Infoblox has not named the vendor.
- The Register's sources said some customer NIOS configuration snapshots were taken. The paper also said it had seen a CEO email describing employee and dependent personal and financial details among the compromised records.
- Infoblox said it has no indication that its products, cloud services, software updates, or build-and-release processes were involved.
- Limit and time-box vendor access to Microsoft 365 and SharePoint. Review guest accounts and tokens when a migration ends.
Infoblox confirmed on Monday, November 16, that attackers reached company information through a compromised third-party data migration vendor. The networking and security firm said it is still investigating the event. A spokesperson said the company immediately activated its incident response procedures. The firm took steps to contain the incident. Infoblox is working with outside cybersecurity experts to understand the scope.
TechCrunch reported that an Infoblox notification described the vendor as one that provides SharePoint data migration services. The Register, citing sources, said the vendor had trusted access to Infoblox's SharePoint system. Those sources said the attackers used the vendor's accounts to copy data directly from that system. Infoblox has not named the vendor.
The Register's sources said the copied files included configuration information from some customers' NIOS deployments. Those files were described as saved snapshots of network data, such as DNS and DHCP configurations, Grid databases, and reporting logs. The paper said such snapshots can be used to recover an appliance or a grid after a failure.
The Register also reported that it had seen an email from CEO Scott Harrell to employees. According to the paper, that message said compromised details included direct deposit information, contact information, dates of birth, and Social Security numbers for employees and dependents. Infoblox told The Register it has sent notifications and is providing support as appropriate. The company declined to say how many employees or customers were affected.
Infoblox said it has no indication, based on its investigation to date, that any of its products, cloud services, software updates, or build-and-release processes were involved. That distinction matters. A break-in through a vendor's access to stored files is serious. It is not the same as a compromise of the software that customers install.
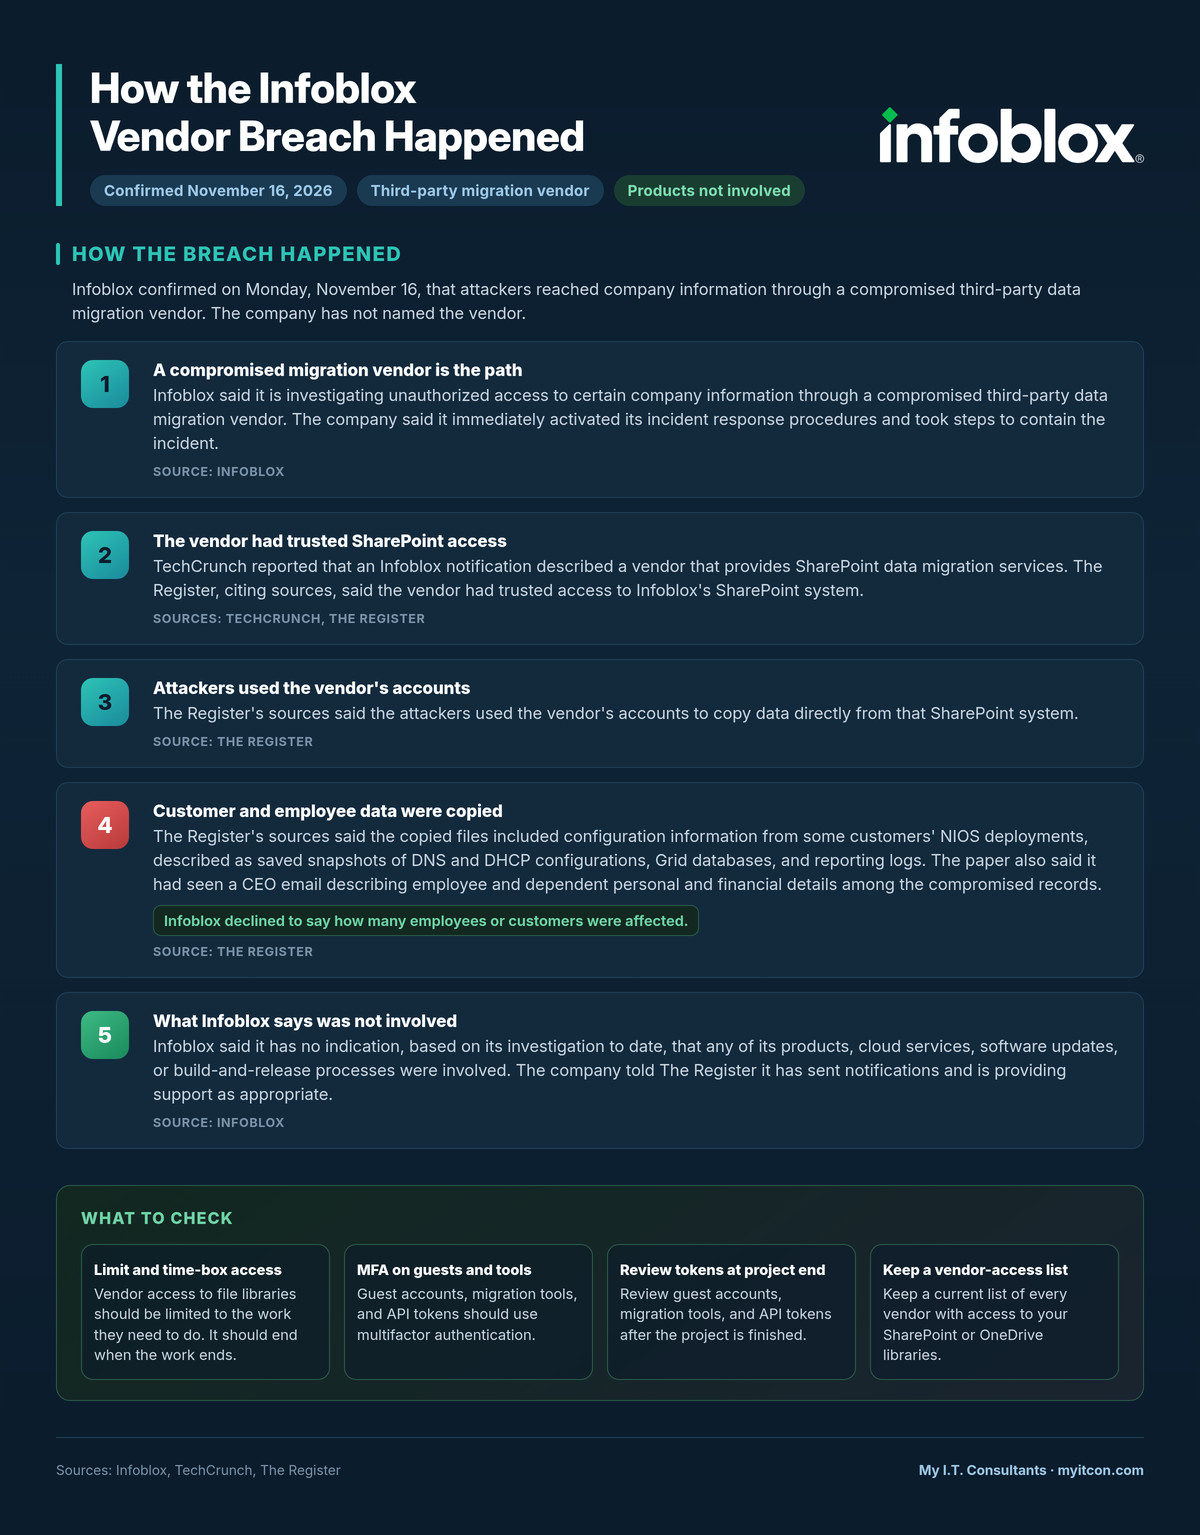
Vendors that help with a Microsoft 365 or SharePoint migration often receive broad, temporary rights to file libraries. That access should be limited to the work they need to do. It should end when the work ends. Guest accounts, migration tools, and API tokens should use multifactor authentication. They should be reviewed after the project is finished. A current list of every vendor with access to your SharePoint or OneDrive libraries is a practical place to start.
If your business is an Infoblox customer, watch for any notice from the company. The investigation is still underway. Anyone who stores network backups or identity records in SharePoint should treat those libraries as sensitive. Keep them off shared spaces that outside accounts can reach, unless that access is required and tightly controlled. The Register reported that Infoblox staff were warned to watch for phishing and other suspicious contacts. That same habit is useful after any vendor incident.
Palestine businesses can ask veteran-owned My I.T. Consultants in Athens for a Free Assessment. As a Microsoft-certified MSP, we can review the vendors with access to your Microsoft 365 and SharePoint environment. Call 903-675-5431. Our office hours for hourly work are Monday through Friday from 7:00 a.m. to 6:00 p.m. Contract customers can reach us 24/7.
Want help with this at your business? See Cybersecurity on our Services page or contact My I.T. Consultants.
Image: My I.T. Consultants, with the official Infoblox logo identifying the company in the story.