SonicWall firewall owners have a patch available for a newly listed SSL-VPN login weakness. The practical next step is to confirm the appliance’s SonicOS version before arranging the appropriate update. CISA added CVE-2026-19868 to its Known Exploited Vulnerabilities catalog on November 6.
The flaw affects the SSL-VPN service in SonicOS, the software running on SonicWall firewalls. It applies to deployments with SAML enabled for SSL-VPN logins. SAML connects that sign-in process to an organization’s identity provider.
The weakness concerns an alternate route into the VPN. A user with valid credentials for another authentication method may bypass the SAML controls. Successful exploitation may also bypass multifactor authentication enforced through SAML. This is not a claim that every SonicWall login or every form of MFA can be bypassed. Valid alternate-method credentials are part of the documented condition.
SonicWall’s advisory lists SonicOS 7.3.4-7013 or later as the fix for Gen7 firewalls. It lists 8.2.3-8015 or later for Gen8 firewalls. Affected versions include 7.3.3-7015 or earlier on Gen7, plus 8.2.2-8015 or earlier on Gen8. Your IT provider should still match the exact model against that advisory before choosing firmware.
This is a different product line from the SMA1000 remote-access appliances involved in September’s separate zero-day coverage. An earlier SMA1000 hotfix should not be mistaken for this SonicOS update.
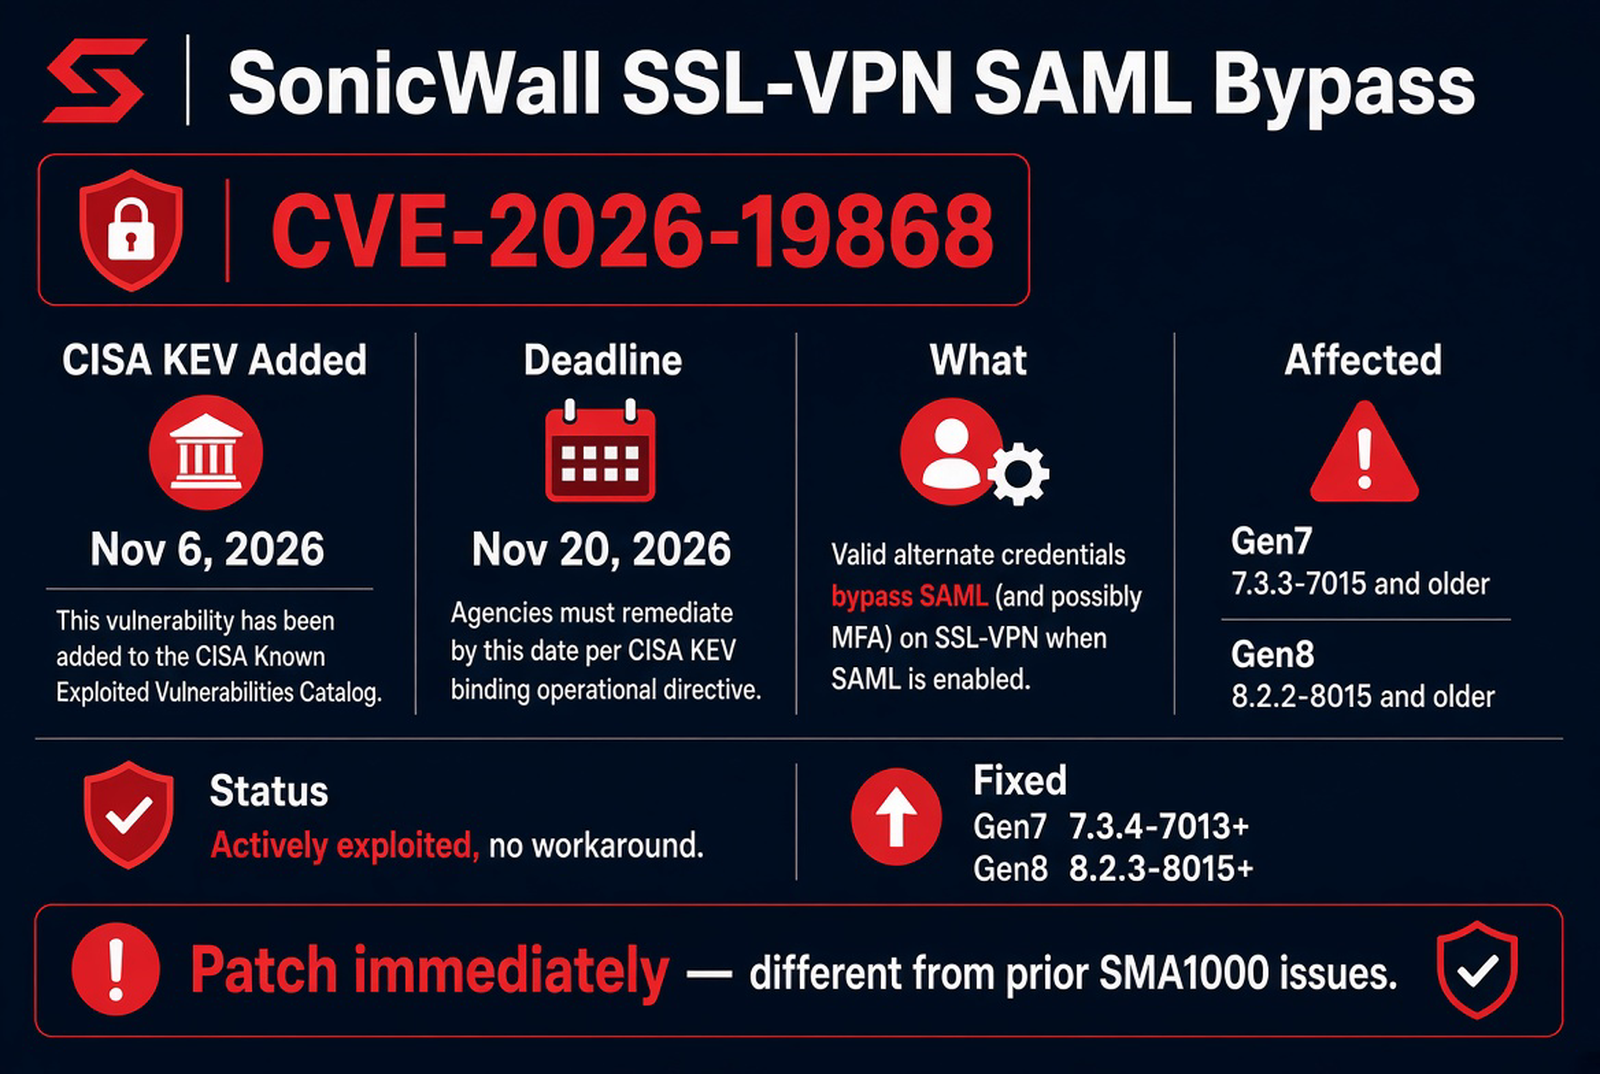
CISA says its listing is based on evidence of active exploitation. SonicWall’s quoted statement is narrower: its security team investigated a report indicating potential exploitation. The available reporting does not establish that any particular business was compromised. CISA’s November 20 remediation deadline applies to federal civilian executive branch agencies, not automatically to private Texas businesses.
For business owners, the useful question is whether remote access follows the protections you expect. Ask your IT provider to verify the installed firmware after updating. Have them review the SAML identity-provider settings against the intended MFA policy. Unused SSL-VPN access should be disabled. Necessary access should have the narrowest practical exposure. Continue watching SonicWall’s advisory for changes. These checks support the update; they are not a substitute for it.
Canton businesses can ask veteran-owned My I.T. Consultants in Athens for a Free Assessment of their East Texas technology needs. Call 903-675-5431 Monday through Friday from 7:00 a.m. to 6:00 p.m.
Want help with this at your business? See Cybersecurity on our Services page or contact My I.T. Consultants.
Image: My I.T. Consultants (original illustration; official SonicWall mark).